Level-orientated user management
With level-based user administration, you assign each user group an authorisation level between 0 and 999. The higher the authorisation level of a user group, the more rights it theoretically has in the application.
You also assign a corresponding authorisation level to each control that can be used to make entries. When a user logs into the application, the authorisation level of the user group of the logged-in user is communicated to all controls. These decide whether they are activated (release of the control < authorisation level of the user group of the user) or deactivated (release of the control > authorisation level of the user group of the user) based on their release level.
The distribution of authorisation levels enables the creation of a user hierarchy. A user group always has all the rights of the user groups that have a lower authorisation and also other rights that user groups with a lower authorisation level do not have.
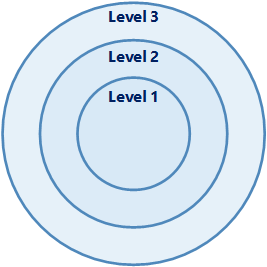
This system usually replicates the employee hierarchy of a company: a superior has all the rights of his subordinates and also the rights assigned to him. His superior has slightly more rights and so on.
Related topics: